
More project photos (2)
The problem
Anyone who has fought with slow Wi-Fi in a crowded apartment building has met the real problem this project addresses: dozens of access points shouting over each other on the same channels, with no visibility into which channel is actually free. Consumer devices just show signal bars; they never show that your router and four neighbors are all piled onto channel 6, or that a network claims WPA2 but is really running the broken WEP protocol. A proper Wi-Fi scanner exposes the radio facts — SSID, BSSID, RSSI in dBm, channel, band, width, security suite, vendor OUI — and aggregates them into channel utilization views that make congestion obvious. This project implements that as a real desktop application with passive scanning, live signal history, neighbor analysis and CSV export.
How it works
- The app puts the wireless adapter into scan mode and issues channel-by-channel probe sweeps, collecting 802.11 beacon and probe-response frames.
- Each frame is parsed for SSID, BSSID, RSSI, channel, band, channel width, supported rates and the RSN information element describing security.
- The vendor is resolved from the BSSID's OUI prefix against a local lookup table.
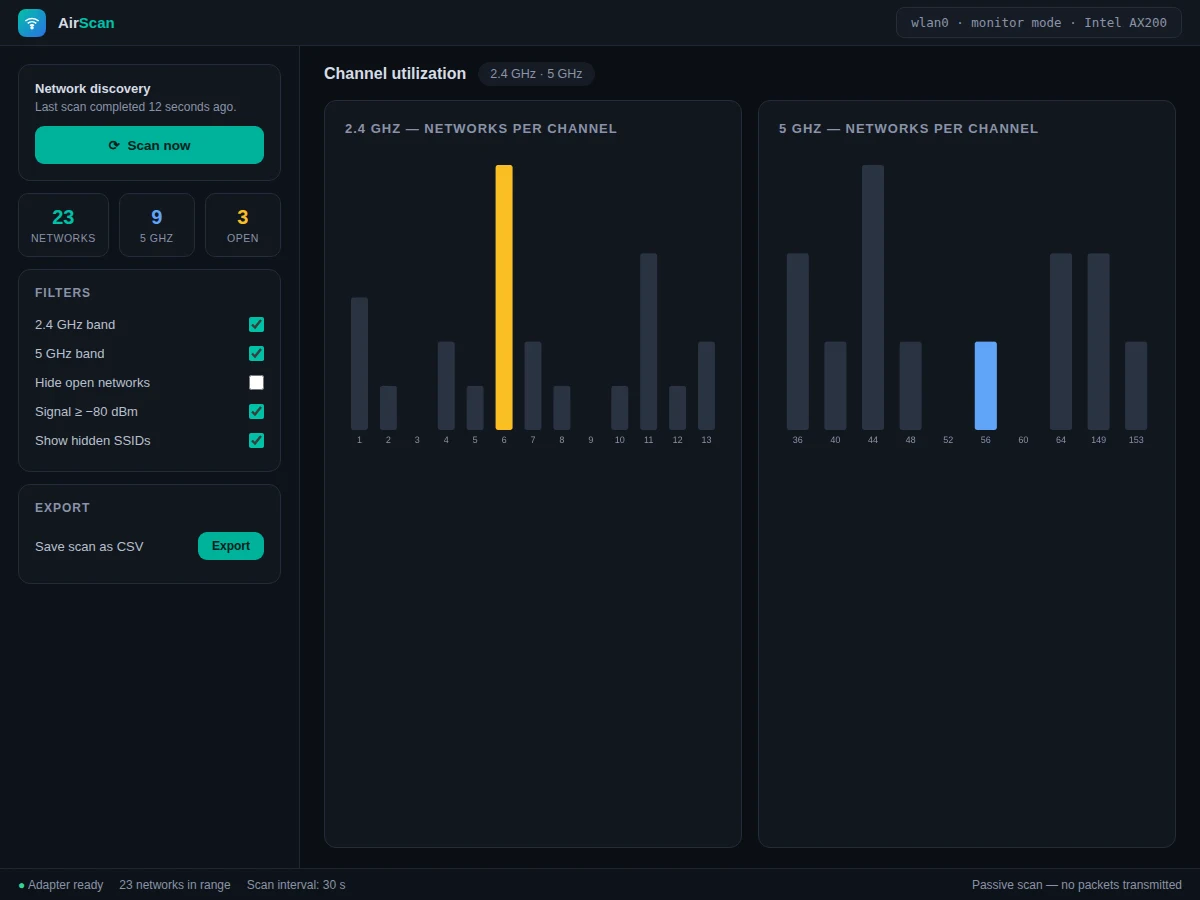
- Results are aggregated per channel to build the utilization graphs, counting networks and weighting by signal strength.
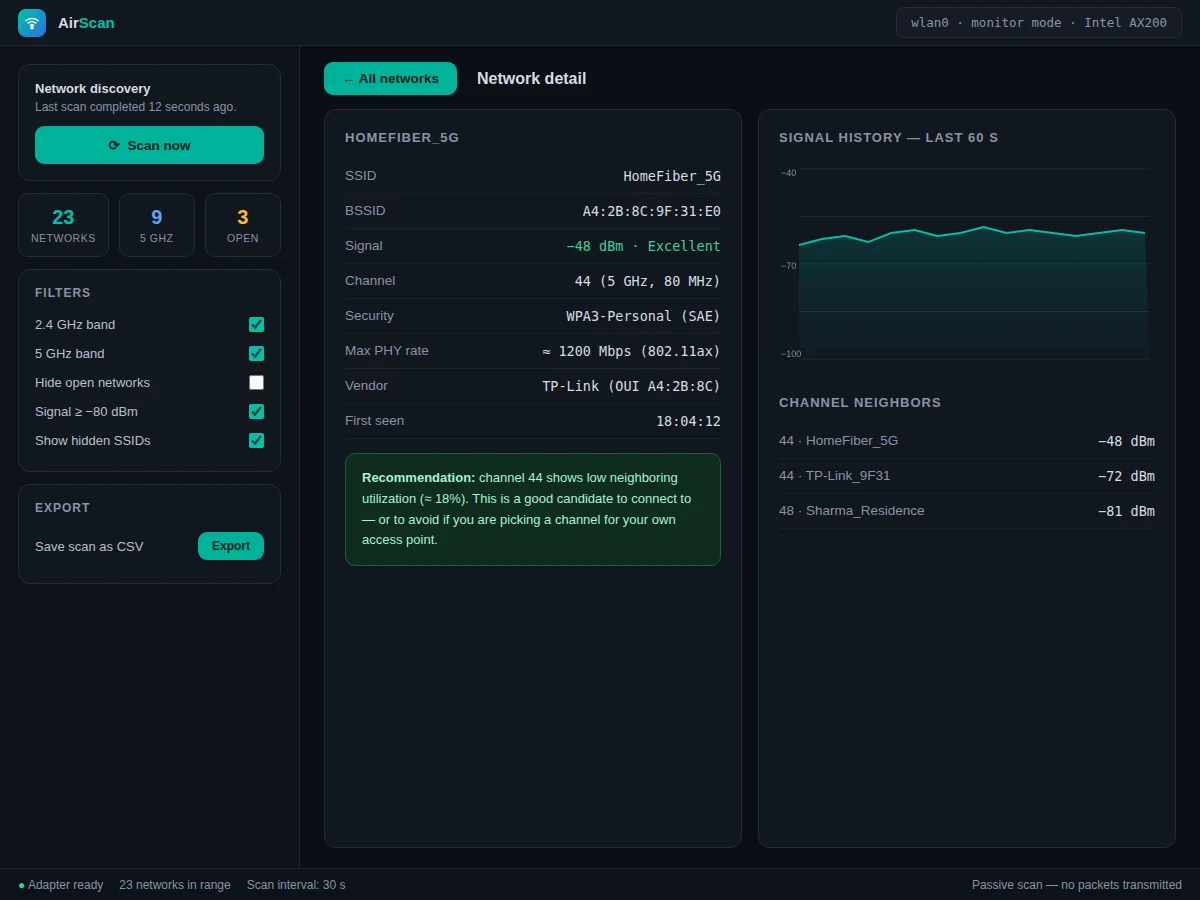
- Selecting a network starts a 60-second RSSI sampler that plots signal history and refreshes the neighbor list on that channel.
- Scans can be exported to CSV with timestamps for before/after comparisons when repositioning an access point.
Tech stack:
- Python 3
- PyQt6 · Qt (desktop UI)
- Scapy (802.11 frame parsing)
- SQLite (scan history)
- OUI vendor database
- Matplotlib-style custom canvas graphs
- PyInstaller (packaging)
| Parameter | Value |
|---|---|
| Platforms | Linux (full), Windows/macOS via adapter APIs (expected) |
| Bands | 2.4 GHz (ch 1–13), 5 GHz (ch 36–165) |
| Scan mode | Passive + active probe sweeps |
| Signal range | −30 to −95 dBm typical display |
| History window | 60 s rolling RSSI plot |
| Export | CSV with full per-network detail |
| Adapter requirement | Any adapter with monitor/scan support |
| Packaging | Single-file installer per OS |
Project features
- [Passive network discovery] Scans all 2.4 GHz and 5 GHz channels for beacon frames and lists every in-range access point with SSID and BSSID.
- [Signal strength in dBm] Real RSSI values with quality grading (excellent/good/fair/poor) instead of vague bars, sortable across networks.
- [Security auditing] Identifies WPA3, WPA2, open and legacy WEP networks at a glance, flagging weak configurations worth avoiding.
- [Channel utilization graphs] Per-band bar charts show how many networks crowd each channel, making the least-congested choice obvious.
- [Signal history tracking] Select a network to watch its RSSI plotted over the last 60 seconds — useful for finding dead spots by walking around.
- [Neighbor analysis] Lists co-channel and adjacent-channel networks with their signal levels to explain interference on a chosen channel.
- [CSV export] Save any scan with full details for reports, site surveys and documentation.
What is included
- Complete desktop application source code
- Installer and adapter setup guide
- Site-survey walkthrough document (how to read the graphs)
- Project report PDF (802.11 scanning, dBm math, channel overlap, security suites)
- PPT presentation for final review
- Viva Q&A preparation document (beacon frames, RSSI vs bars, WPA2 vs WPA3, channel bonding)
Limitations & prerequisites
- The app is strictly passive — it never deauthenticates, cracks or connects to networks it does not own; it is a survey tool, not a penetration tool.
- Hidden SSIDs are shown as reported by probe responses; the app does not attempt to force their disclosure.
- 6 GHz (Wi-Fi 6E) needs a 6E-capable adapter and is supported only where the OS exposes the band.
- RSSI values vary between adapter chipsets — use them comparatively on one machine, not as absolute lab figures.
- Windows and macOS restrict raw monitor mode, so some advanced views are richest on Linux.
- Signal history is a 60-second rolling window, not a long-term logger.
Frequently Asked Questions
Is this a hacking tool?
No. It only reads the beacon frames that access points broadcast publicly every ~100 ms — the same information your phone uses to draw its Wi-Fi list. It cannot crack passwords or disrupt networks.
How do I use it to fix slow Wi-Fi?
Open the channel utilization graph, find the least-crowded channel on your band, and move your own router there — the report walks through this as a worked site-survey example.
What does −70 dBm mean?
dBm measures received power on a logarithmic scale; closer to zero is stronger. Roughly: −50 is excellent, −60 good, −70 fair, −80 weak, below −85 barely usable. The app grades these automatically.
Why do channels matter so much on 2.4 GHz?
Each 2.4 GHz channel is 20–22 MHz wide but spaced only 5 MHz apart, so only channels 1, 6 and 11 avoid overlapping — the graph makes this overlap visible.
Can it detect rogue or fake access points?
It surfaces anomalies worth investigating — duplicate SSIDs on unexpected BSSIDs, open twins of secured networks — and exports the evidence to CSV.
Is this project suitable for a final-year project?
Yes — for Computer Science and IT programs. It teaches 802.11 fundamentals, frame parsing, signal analysis and responsible, legal wireless surveying. Suitable for B.E./B.Tech final-year projects in Computer Science and IT.
Components & software requirements
- Python 3
- PyQt6 · Qt (desktop UI)
- Scapy (802.11 frame parsing)
- SQLite (scan history)
- OUI vendor database
- Matplotlib-style custom canvas graphs
- PyInstaller (packaging)
Delivery information
Built-to-order project. Delivery timeline is shared after order confirmation based on current queue.
Support terms
Complete documentation, setup guide, and viva preparation included. Support for setup and explanation provided.